Decisions under attack,
rehearsed before the breach.
Readiness. Empowered.
Infiniqo runs cybersecurity tabletop exercises and incident response simulations that turn your runbooks into living rehearsals, ransomware, supply-chain compromise, insider misuse, so executives, SOC analysts and counsel rehearse the call you cannot afford to get wrong.
The readiness gap
Controls Are Audited. Decisions Are Not.
Security programs prove their tooling. Few prove how leaders decide once the alarm sounds.
Threat velocity
Attacks escalate in hours; approval chains still move in days.
Disclosure scrutiny
SEC, NIS2 and DORA clocks start before facts are complete.
Siloed response
Security, legal and comms each hold part of the picture.
When reality changes, the question changes.
Can leadership decide well while under attack?
GTaaS turns tabletop exercises from occasional events into a repeatable way for leadership teams to practice difficult decisions together.
Organizational readiness
From Alert to Defensible Decision
Runbooks describe steps. Rehearsal proves the team can take them.
- 01DetectCorrelate the signal and size the incident fast.
- 02EscalateConvene the right executives without delay.
- 03CommandAlign security, legal, comms and the business.
- 04DecideContain, pay, disclose: choose under uncertainty.
- 05DefendShow regulators and insurers why you acted.
Buyer profiles
Accountable for the breach call.
Built for the people accountable when the breach call goes wrong, and for the leaders who must prove preparedness before it does.
Outcomes
What changes.
Measured against what boards, regulators and insurers now ask after an incident.
Mean Time to Decide
Compress critical decisions from hours to minutes through rehearsed muscle memory.
Board Confidence
Audit-grade evidence of cyber preparedness across every business unit.
Regulatory Posture
Tested-plan evidence for SOC 2 (CC7.1, CC7.2), NIST CSF and SP 800-61, PCI DSS, NIS2, DORA, SEC disclosure, HIPAA, ISO 27001, CMMC and FedRAMP.
Cross-Functional Fluency
SOC, legal, comms and the C-suite responding as one trained team.
Situation Rooms
Rehearse the Breach Before It Rehearses You
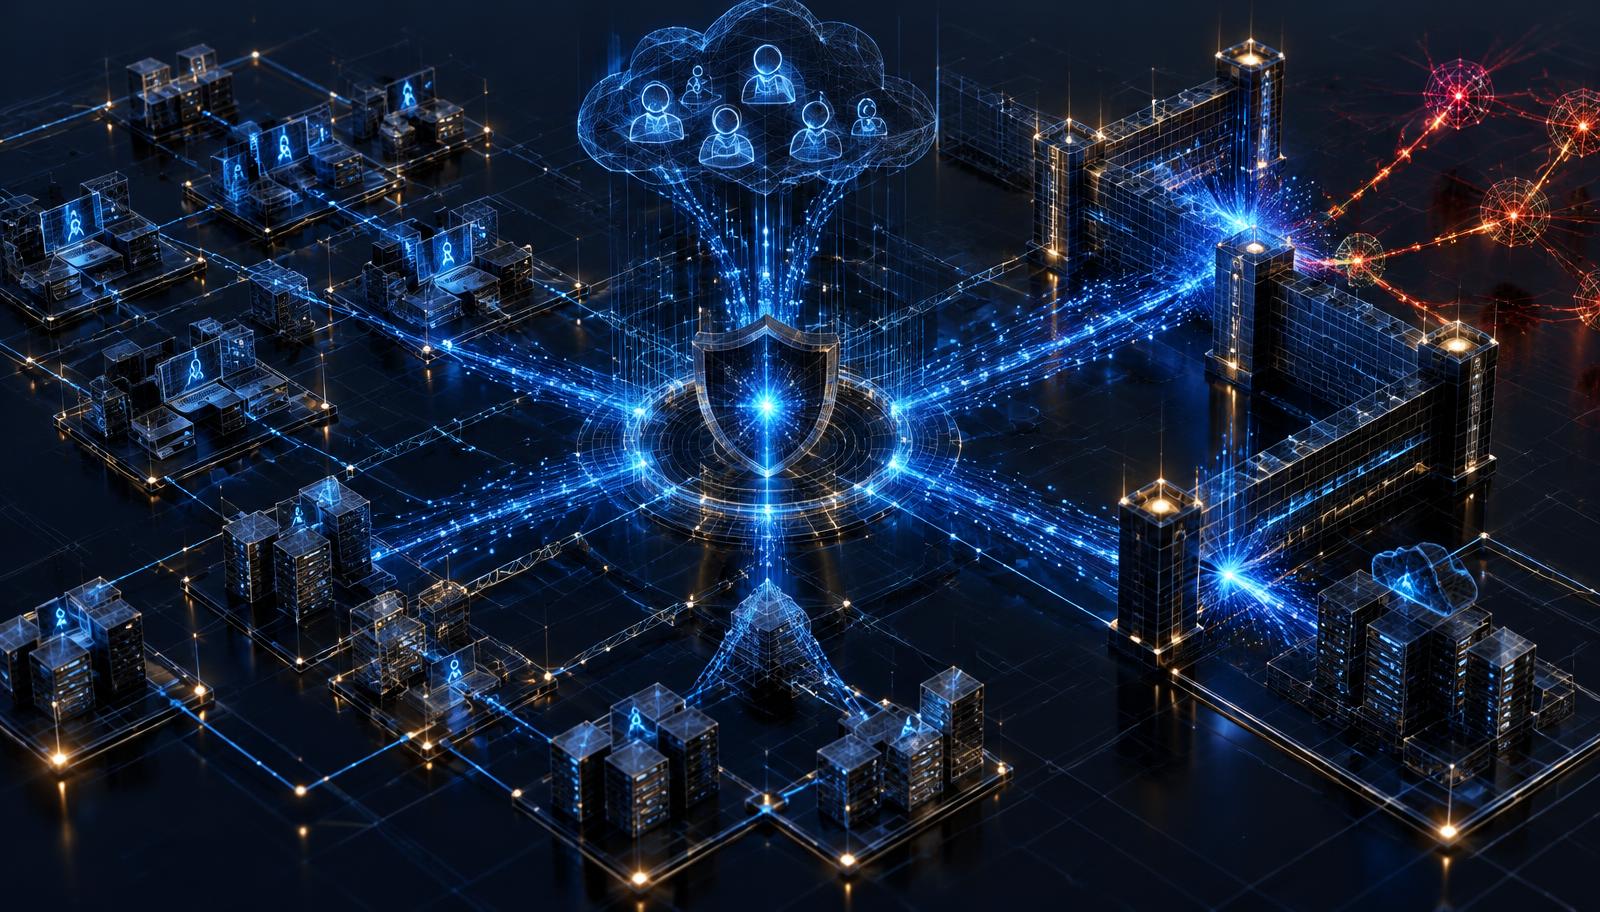
One configuration of the Infiniqo Situation Room architecture. See the architecture →
Ransomware & Extortion Room
Examples
- Encrypted core systems
- Data leak threat
- Payment decision
- Insurer engagement
Measures
Containment speed · Escalation · Payment governance
Third-Party Compromise Room
Examples
- Vendor software breach
- Cloud provider outage
- Shared credential abuse
Measures
Dependency mapping · Vendor coordination · Customer notice
Executive Disclosure Room
Examples
- Materiality call
- Regulator notification
- Board briefing
- Public statement
Measures
Disclosure timing · Message discipline · Record quality
Where AXON fits
Rehearse in Prepare. Run in Respond.
Run live
AXON Respond
Run the live incident in one shared environment: brief, decide, act and seal evidence for regulators, insurers and the board as it happens.
Explore AXON Respond →Rehearse
AXON Prepare
Rehearse ransomware, data exfiltration and third-party breach scenarios with executives, IT and legal, and close the gaps before an attacker finds them.
Explore AXON Prepare →Partnership models
Partner With Infiniqo
Enterprise Direct
- Annual rehearsal program
- Board and SOC tracks
- Quarterly evidence reports
MSSP & IR Partners
- White-label tabletop delivery
- Retainer value-add
- Shared readiness scoring
Cyber Insurers
- Portfolio readiness signal
- Pre-bind rehearsal
- Renewal evidence
Advisory Firms
- Co-delivered exercises
- Framework-mapped debriefs
- Client readiness benchmarks
Scenarios
A sample of the work.
- Ransomware extortion with public disclosure pressure
- Third-party software supply-chain compromise
- Insider data exfiltration during M&A
- Cloud identity takeover and lateral movement
- OT / critical infrastructure intrusion
Frequently asked
Questions, answered.
Question 01
How long does a typical tabletop exercise take?
Most exercises run two to four hours in a single intensive session, though multi-day deep dives are available for complex organizational structures. We design the arc so that momentum builds and key decision points surface naturally, not rushed, never dragging.
Question 02
Who should participate in the simulation?
We recommend a cross-functional cell: CISO, legal counsel, communications lead, business-unit heads and SOC representation. The magic happens when these functions discover, in real time, how their silos affect collective response speed.
Question 03
How is this different from a penetration test or audit?
Pen tests find holes; audits check boxes. Our simulations rehearse the human decisions that happen after the alarm sounds, who calls whom, what you say, when you escalate, how you document. It is muscle memory for crisis, not a vulnerability scan.
Question 04
What deliverables do we receive after the exercise?
You receive a decision timeline annotated with every pivot point, a gap analysis mapped to your frameworks of choice, and a rehearsed playbook you can circulate to new hires the next day.
Question 05
Can scenarios be tailored to our specific threat landscape?
Every scenario is built from your threat intelligence, your crown jewels and your recent incident history. We do not use off-the-shelf scripts. The ransomware note in the simulation will bear your company's name.
Question 06
Which frameworks does the exercise evidence support?
Many frameworks now ask for proof that the incident response plan has been tested, not just written. SOC 2 CC7.1 and CC7.2 auditors ask for that evidence every year; PCI DSS 12.10 requires annual testing of the response plan; NIST CSF and SP 800-61 describe testing and lessons learned; CMMC and FedRAMP expect tested incident response for defense and federal work; NIS2, DORA, SEC disclosure, HIPAA and ISO 27001 cover the regulated and international side. Each exercise produces a dated, sealed record you can hand to the auditor.
Question 07
How often should we run these exercises?
Twice yearly is the baseline for regulated industries; quarterly for organizations with elevated threat exposure. We also recommend a refresher within thirty days of any material organizational change, M&A, new leadership, major cloud migration.
Question 08
What scenarios are covered?
Representative scenarios include: Ransomware extortion with public disclosure pressure; Third-party software supply-chain compromise; Insider data exfiltration during M&A; Cloud identity takeover and lateral movement; OT / critical infrastructure intrusion.
- Most exercises run two to four hours in a single intensive session, though multi-day deep dives are available for complex organizational structures. We design the arc so that momentum builds and key decision points surface naturally, not rushed, never dragging.
- We recommend a cross-functional cell: CISO, legal counsel, communications lead, business-unit heads and SOC representation. The magic happens when these functions discover, in real time, how their silos affect collective response speed.
- Pen tests find holes; audits check boxes. Our simulations rehearse the human decisions that happen after the alarm sounds, who calls whom, what you say, when you escalate, how you document. It is muscle memory for crisis, not a vulnerability scan.
- You receive a decision timeline annotated with every pivot point, a gap analysis mapped to your frameworks of choice, and a rehearsed playbook you can circulate to new hires the next day.
- Every scenario is built from your threat intelligence, your crown jewels and your recent incident history. We do not use off-the-shelf scripts. The ransomware note in the simulation will bear your company's name.
- Many frameworks now ask for proof that the incident response plan has been tested, not just written. SOC 2 CC7.1 and CC7.2 auditors ask for that evidence every year; PCI DSS 12.10 requires annual testing of the response plan; NIST CSF and SP 800-61 describe testing and lessons learned; CMMC and FedRAMP expect tested incident response for defense and federal work; NIS2, DORA, SEC disclosure, HIPAA and ISO 27001 cover the regulated and international side. Each exercise produces a dated, sealed record you can hand to the auditor.
- Twice yearly is the baseline for regulated industries; quarterly for organizations with elevated threat exposure. We also recommend a refresher within thirty days of any material organizational change, M&A, new leadership, major cloud migration.
- Representative scenarios include: Ransomware extortion with public disclosure pressure; Third-party software supply-chain compromise; Insider data exfiltration during M&A; Cloud identity takeover and lateral movement; OT / critical infrastructure intrusion.